Our Partners




Empowering Ideas, Inspiring Solutions
Empowering Ideas, Inspiring Solutions
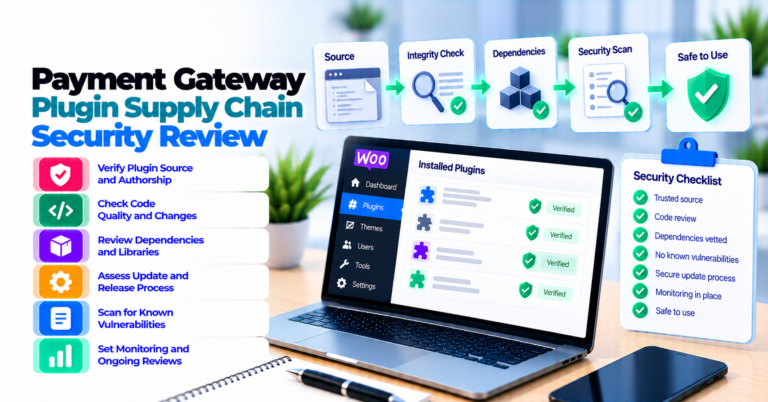
Review payment gateway plugin maintainers, provenance, dependencies, build and update channels, vulnerability response, EOL, and rollback before checkout.
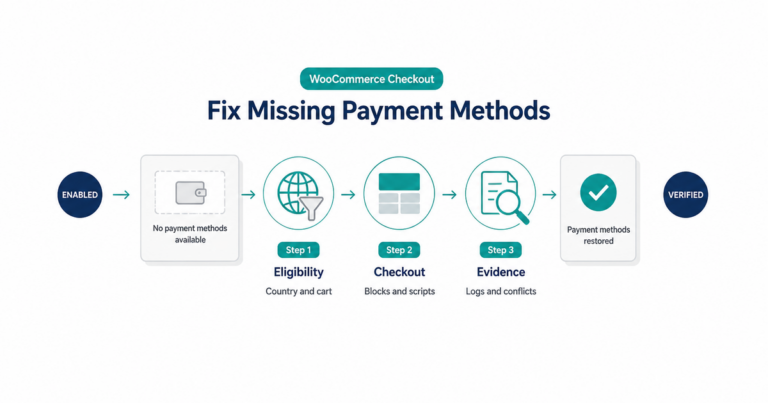
Fix “no payment methods available” in WooCommerce with checks for settings, location, currency, shipping, Blocks, cache, logs, and conflicts, step by step.
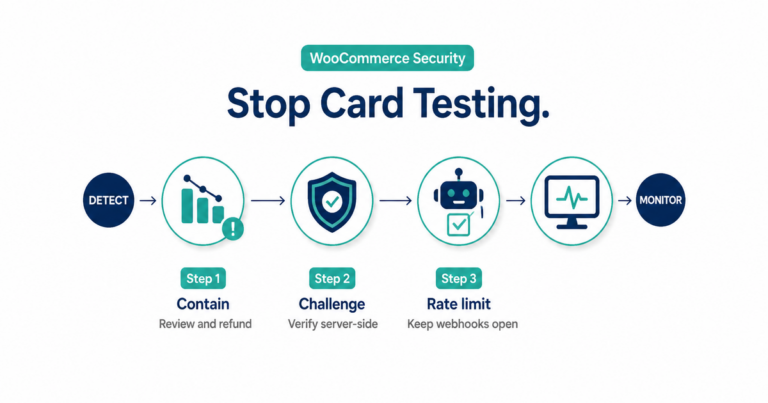
Spot a WooCommerce card testing attack, contain fraudulent orders, refund successful tests, and add layered bot controls without blocking real shoppers.
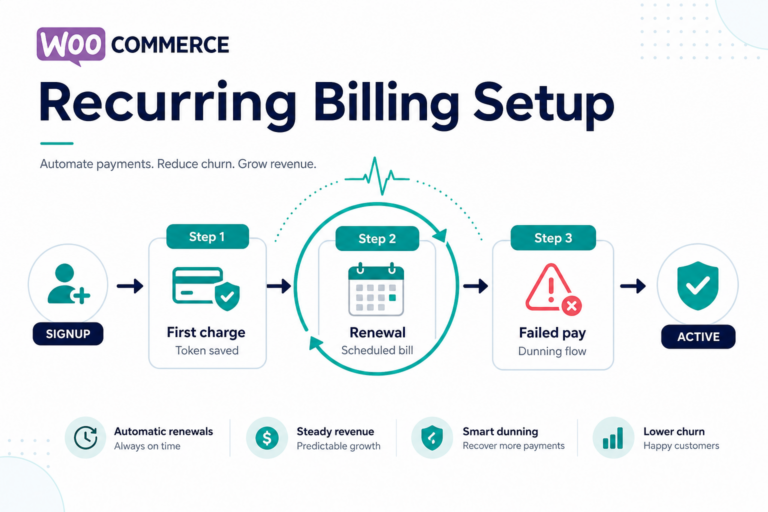
Recurring billing depends on tokens, retry logic, and gateway—not just the WooCommerce Subscriptions plugin. Here is what to verify before you launch.
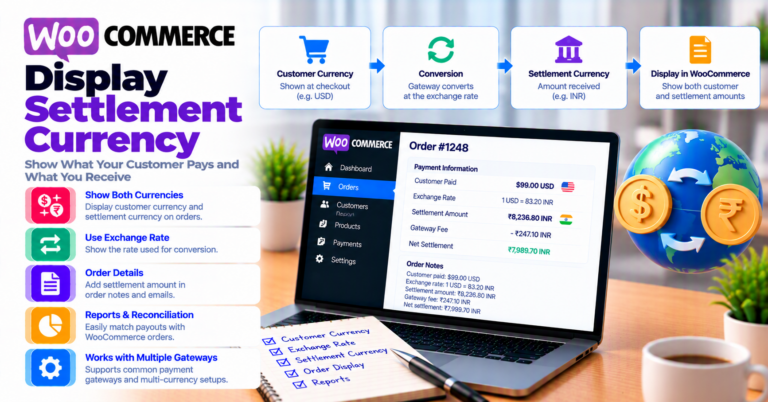
Shoppers may pay in EUR while you settle in USD—FX spreads, refunds, and reporting all behave differently. Map display vs settlement before going multi-currency.
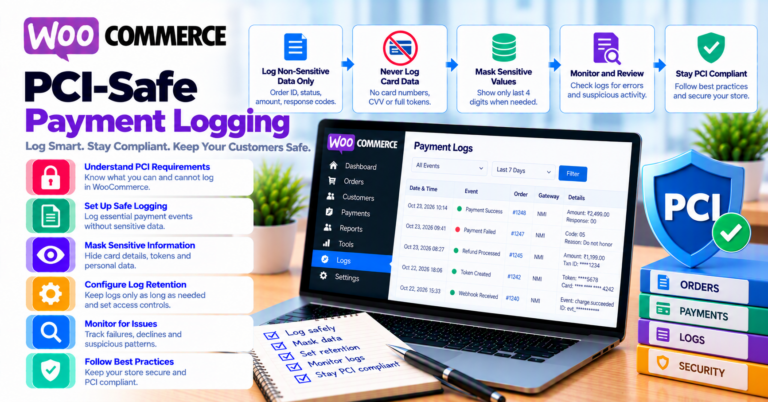
Good logs fix failed payments fast; bad logs create PCI scope and breach risk. Learn what belongs in order notes, server logs, and support tickets.
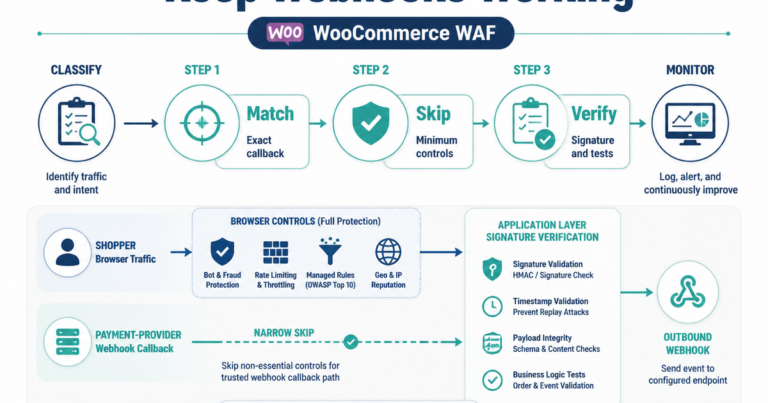
Protect WooCommerce checkout with WAF rules while keeping signed payment webhooks reachable. Classify paths, scope skips, test retries, and monitor events.
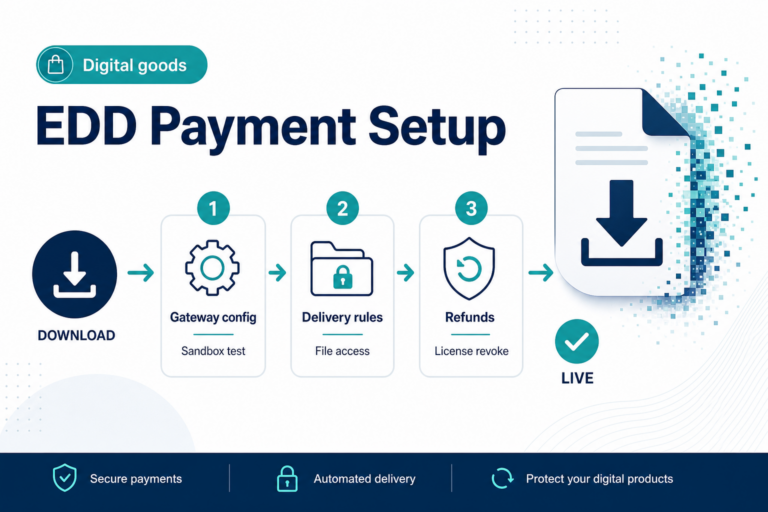
Align Easy Digital Downloads with your payment gateway so customers receive files or licenses immediately—and refunds and disputes stay traceable.
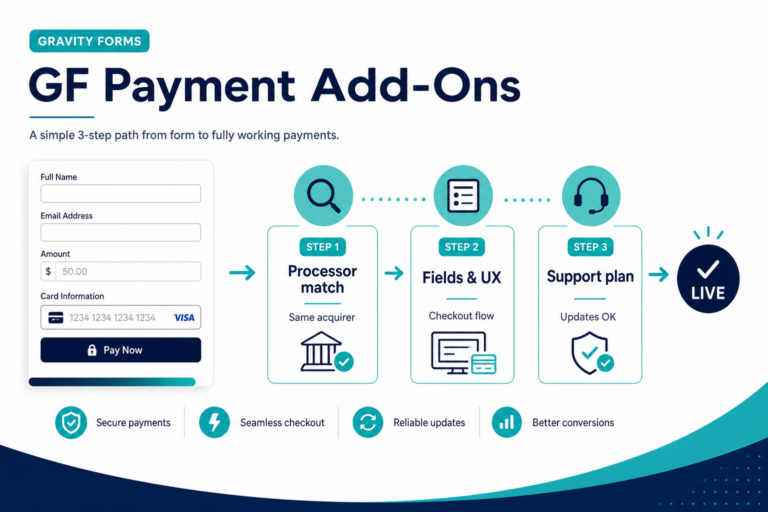
Compare processors, hosted vs direct flows, recurring billing, refunds, and regional coverage before you buy a Gravity Forms payment integration.
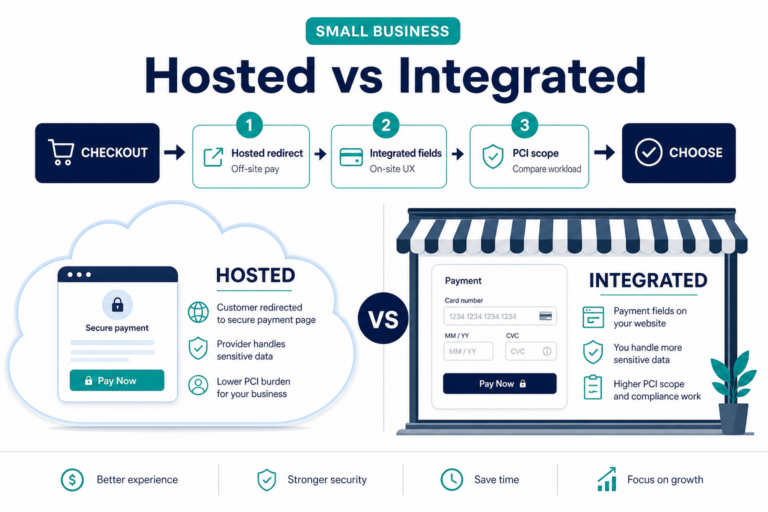
Compare hosted (redirect, hosted fields) and integrated checkout for small businesses: PCI scope, UX, dev cost, and when each fits WooCommerce or Gravity Forms.